Decima Systems // AI-assisted security testing
Est. 2026 / Scoped, authorised, logged
Scoped pilot assessments / Pilot enquiries open
A standing AI adversary for your infrastructure. Follow the investigation, inspect the evidence, and give your team a clear route from finding to verified fix. Reviewed reports turn that work into a record your security team and board can use.
Set up your account in minutes. Testing starts once scope, authorisation and your internal approvals are in place, at the scheduled start when a worker and sufficient funds are available. Your coverage, model choice and testing budget set the cadence—from scheduled runs toward continuous operation.
Engagement parameters
| Mission | Continuous validation |
| Testing | Cadence set by your budget |
| Reporting goal | Daily, downloadable updates |
| Onboarding | Self-service account setup |
| Activation | Agreed scope + approvals |
01 / The assessment
Find the path. Prove the fix.
A useful assessment connects a weakness to its impact and the change that closes it. This is the workflow we’re building Decima around.
01
Scope. Agree the application, permitted tests, credentials and test window.
02
Test. Investigate how exposed services, application flaws and permissions connect.
03
Verify. Reproduce the finding, collect evidence and have a person review the claim.
04
Retest. Confirm the fix and carry its status into the next daily report.
Daily reporting is the goal. Each finding keeps its evidence, test date and remediation history.
03 / Services
Start with one real question.
Can this application be compromised—and can we show that the fix works? Start there. Expand coverage as the testing earns your confidence.
| Code | Service | Detail | Availability | Scope |
|---|---|---|---|---|
| PT-01 | Application & API assessment | The first pilot: one agreed application or API estate, investigation of exploitable weaknesses, a reviewed report and one retest. Scope and readiness determine the start date. | Pilot enquiries | Defined scope |
| AI-02 | AI agent & LLM assessmentPilot focus | A proposed pilot focus for applications using agents: prompt injection, tool permissions and access to sensitive data. Agree which components and attack scenarios the assessment can cover. | Scoped with pilot | Application layer |
| RP-03 | Daily security & compliance reports | Beautifully typeset PDFs with clear executive analysis, useful charts, verified technical findings and relevant ISO control mappings. Daily editions will preserve the evidence, actual test dates and history of fixes. Built to be read, presented and shared. | In development | Shareable evidence |
| CV-04 | Continuous security validation | A standing engagement that tests, reviews changes and retests fixes. Your testing budget, coverage and model choice determine cadence, from scheduled runs toward continuous execution. Daily report refreshes retain the actual test dates. | Planned | After pilot |
| VD-05 | Managed vulnerability disclosure | A future service for receiving researcher reports, checking scope, reproducing findings and coordinating fixes. It reuses the verification workflow we are developing for our own agents. | Roadmap | Report intake |
| BB-06 | Private bug bounty programs | A later extension with invited researchers, explicit testing rules and a customer-funded reward budget. Decima would manage triage and communication, with human review of reward decisions. | Roadmap | Invitation only |
04 / The output
Live findings. Beautiful reports.
The experience we’re building: a live view of connected weaknesses and verified evidence, paired with beautifully designed PDF reports. Clear analysis, considered typography and visuals your security team can use and your board can understand. The example below uses specimen data.
Attack path DS-4471
Specimen data / Live findings and daily PDF reports in development / One evidence record, ready to explore or share.
The evidence, beautifully resolved
A clear picture.
A powerful report.
Follow the technical detail. See the business consequence. Put a beautifully considered report in the hands of your board, security team and auditors.
Explore our 38-page sample: executive decisions, attack paths, detailed findings and evidence of the fix.
Explore the sample report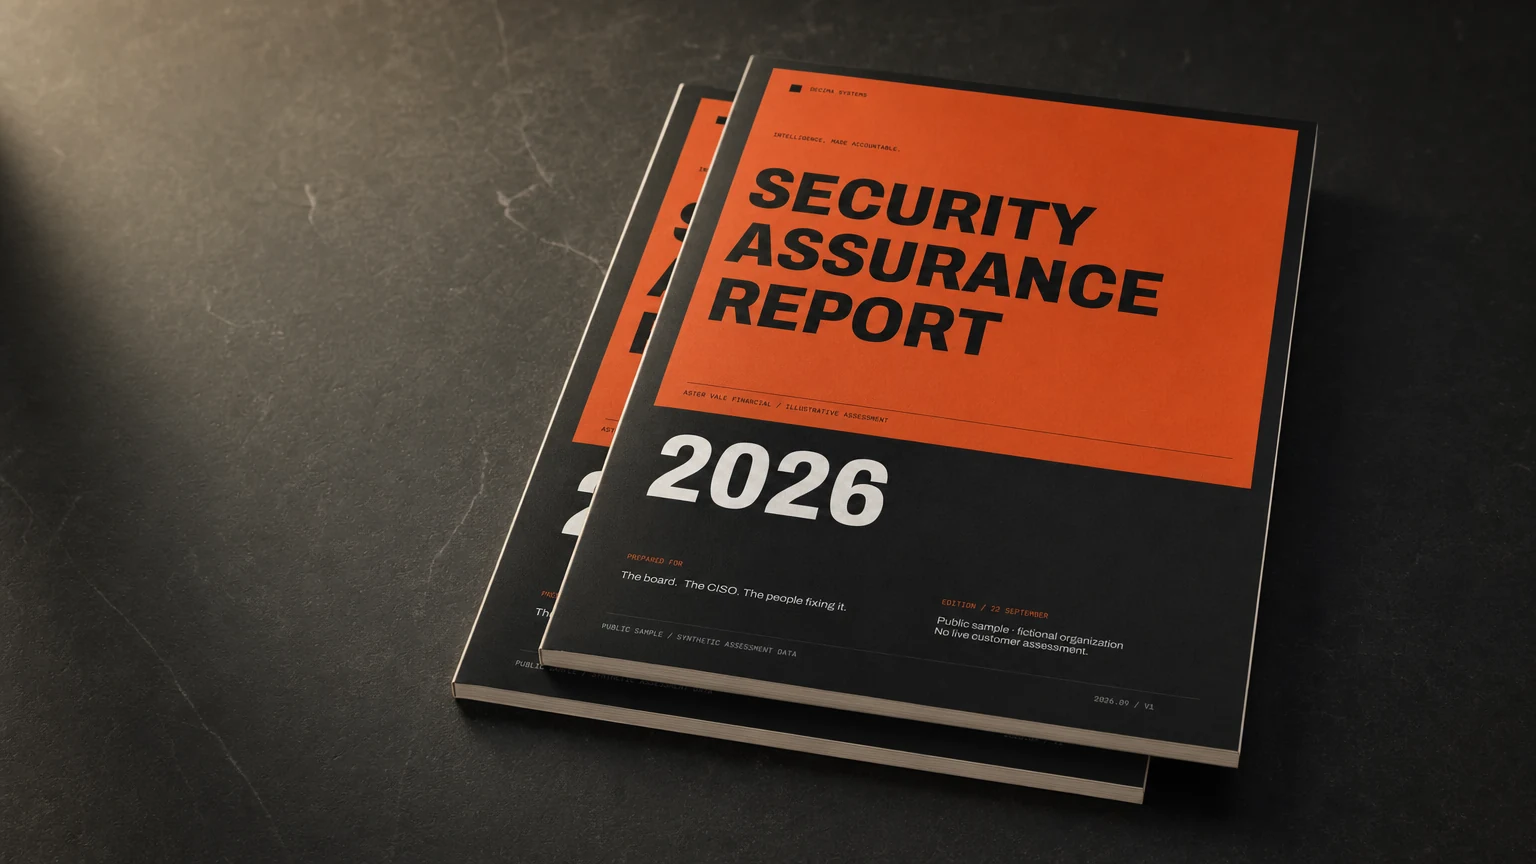 Inside the report
38 pages / 12 detailed findings / One traceable story
Fictional assessment. Synthetic data. AI-staged photograph of the sample report.
06 / Terms
Your scope. Your cadence. Your budget.
Indicative pilot and recurring pricing. Set up quickly, agree your requirements and confirm readiness before testing begins.
Pilot
$3,000
one scoped assessment
Start with one application or API. Agree the question, investigate the risk and verify the fix.
- ■One agreed application / API estate
- ■Defined scope and testing window
- ■Reviewed findings and business impact
- ■Practical remediation guidance
- ■One agreed retest
Adversary
Standing service$1,499
per month
A standing validation service with daily reporting as its core goal. Your coverage, model and testing budget set the cadence.
- ■Up to 15 registered targets; test scope agreed
- ■Agreed testing and compute allowance
- ■Daily report updates — in development
- ■Validated findings and ISO control mappings
- ■Named reviewer and agreed contact hours
- ■Remediation tracking and defined retests
Sovereign
Bespoke
annual engagement
A planned deployment inside your environment, with dedicated capacity and explicitly agreed data and access controls.
- ■Scope and capacity defined by contract
- ■Customer-perimeter deployment design
- ■Dedicated model and tooling options
- ■Operator access and updates agreed
- ■Reporting and retention requirements agreed
Proposed service scope / Daily reporting in development / Additional testing and premium models quoted separately. Activation follows authorisation and your required approvals. Excludes applicable US sales tax.
07 / Leadership
Lennart Lopin
Decima began as a tool Lennart wanted for his own work as CTO and co-founder of Byte Federal. Operating financial infrastructure brings practical questions into focus: can a finding be reproduced, can engineers fix it, and what evidence supports the result?
His book, No Human in the Loop: Cybersecurity in the Autonomous AI Age, examines the security implications of autonomous agents. Decima carries that research into a product being developed for repeated testing, useful evidence and accountable review.
Relationships across industry, cyber-forensics and universities inform the product direction: keep evaluating new models, learn from practitioners and researchers, and test improvements against real security work. BF’s compliance experience informs that process; its certification does not certify Decima’s product.
“Friday, 14:00 UTC. Five thousand adversarial agents begin their assault. The defenders have twelve humans.”
Opening line / No Human in the Loop
Dossier
| Operating role | CTO & co-founder, Byte Federal |
| Operating experience | Financial infrastructure |
| Certifications | CISSP · CCSP · CSSLP |
| Education | M.A. Computational Linguistics & AI |
| Security programs | ISO 27001 · GLBA experience |
| Published | No Human in the Loop, 2nd ed. |
Decima Research
All perspectivesDefine Autonomous.
Every vendor in offensive security uses the word. Almost none of them mean the same thing by it.. XBOW sells full autonomy. Horizon3 advertises that AI never executes exploits. What the independent research says, and four questions that tell a buyer which machine they are purchasing.
08 / Questions
The ones that actually get asked
01What is Decima being built to do?+
Decima is being built as a standing security-validation service: investigate exploitable weaknesses, verify findings, help engineers fix them and retest the result. Its core design combines specialist AI models, a Kali-style testing environment and human review. Continuous testing and daily, downloadable reporting are central product goals.
02Will testing run continuously?+
Continuous operation is the goal. Your chosen coverage, model and testing budget determine the cadence, from scheduled runs to continuous execution where the agreed capacity supports it. The standing service is designed to maintain daily reports and remediation history between runs. Each report will show when its underlying evidence was last tested.
03What will the daily reports contain?+
Our goal is a live view of findings alongside a beautifully designed daily PDF: an executive narrative, clear charts, verified findings, business impact, technical evidence, fixes and relevant ISO control mappings. We intend to give the PDF the typography and visual care of a premium publication, with downloadable editions and a version history. Each edition will show actual test dates and coverage gaps; a new report does not imply every asset was retested that day.
04How quickly can we onboard and activate?+
Account setup can take minutes. Start with your engagement, scope and planning budget, then download a PDF proposal for your internal approval process. Verify domain control through a manual DNS record when ready. A Cloudflare connection and executive signing through DocuSign are in development. Testing starts only after the final scope, price, permissions, your compliance approvals and our delivery readiness are confirmed.
05What is available today?+
You can create an account, save an engagement plan, choose a planning budget and requested cadence, and download a private PDF budget proposal. Manual DNS verification, a clearly labelled demo console and a 38-page illustrative assessment report are also available. Digital signing, automated assessment execution and daily customer reporting are in development. Pilot enquiries are open; delivery begins after scope, timing and readiness are confirmed.
06Can our compliance team use the reports?+
That is a core purpose of the reporting workflow. We intend to provide evidence, relevant control mappings and a record of findings and fixes that your team can download and share with assessors. Agree required scope, methodology and reviewer qualifications with your assessor before the engagement. A report supports your compliance program; acceptance depends on those requirements. Byte Federal’s ISO certification covers its management system, not certification of the Decima product.
07Will Decima integrate with Vanta or Drata?+
Yes—direct compliance integrations are on the roadmap, starting with Vanta and then Drata as customer demand develops. We plan to send assessment reports and remediation evidence automatically into your connected account, with structured finding sync where the platform supports it. You will choose what is shared and authorize access. The connectors are not available yet; setup will depend on your platform permissions and supported workflows.
08Can we choose the model and where our data goes?+
The intended catalog offers customer choice among evaluated, security-specialized open-weight models, with a recommended default. Self-hosted inference is the intended baseline; rented infrastructure and deployment inside your own perimeter have different data boundaries. We will agree model hosting, tool-output handling, evidence storage and operator access before testing. Customer-perimeter deployment needs a separate scope and validation.
09What do you mean by security-specialized models?+
Our intended model variants combine reduced refusal behavior, sometimes called abliteration, with purpose training for authorized security work. We will evaluate each variant inside the actual testing harness for finding quality, tool reliability, review effort and cost. Reducing refusals does not establish security expertise on its own. New models enter the offered catalog only after evaluation.
10Will you manage vulnerability disclosures or bug bounties?+
Both are on the roadmap. The same verification workflow could reproduce researcher submissions and coordinate remediation. We plan to start with managed disclosure intake, then a private program with invited researchers. A bounty program needs its own scope, response commitments and customer-funded reward budget, separate from the Decima service fee.
11What does it cost?+
Indicative pricing is $3,000 for one scoped application/API pilot with a reviewed report and one retest, followed by $1,499 per month for bounded recurring validation and the planned daily reporting service. Your budget, coverage and model choice determine testing cadence. Wider coverage, additional compute or specialist work needs a separate quote. Recon at $299 per month and custom Sovereign deployments are planned options. Signup alone does not purchase an assessment.